
Webinar: Inside the Novee Gym
Training, Benchmarking, and Controlling Offensive AI That Thinks Like an Attacker.
LIVE WEBINAR | OCTOBER 13 | 10 AM ET
There’s no benchmark for measuring how good AI is at the actual work of offensive security. There’s no single AI model that’s best at every task, and too many AI-driven OffSec systems that treat safety as an afterthought. These are the gaps that Novee sought to close. In this technical fireside chat with Head of AI Dan Padnos and AI Research Team Lead Or Dancig, you’ll find out how we did it.
Tune in to learn about the techniques we use to train our offensive AI, and how we turned those techniques into a public benchmark for agentic greybox testing. You’ll also hear why offensive work needs many models — including small language models, not one frontier LLM — and why these systems have to be built safety-first.
See how offensive AI actually works. Reserve your seat for the technical fireside.
LIVE WEBINAR | OCTOBER 13 | 10 AM ET
There’s no benchmark for measuring how good AI is at the actual work of offensive security. There’s no single AI model that’s best at every task, and too many AI-driven OffSec systems that treat safety as an afterthought. These are the gaps that Novee sought to close. In this technical fireside chat with Head of AI Dan Padnos and AI Research Team Lead Or Dancig, you’ll find out how we did it.
Tune in to learn about the techniques we use to train our offensive AI, and how we turned those techniques into a public benchmark for agentic greybox testing. You’ll also hear why offensive work needs many models — including small language models, not one frontier LLM — and why these systems have to be built safety-first.
Meet the Trainers
AI Research Team Lead at Novee Security, where he leads model training and post-training to build proprietary AI penetration testing models. Former Operations Research Head of Data Science in the IDF; now builds state-of-the-art synthetic environments and benchmarks to sharpen Novee’s autonomous offensive AI stack.
Chosen by teams that take attackers seriously



THE SOLUTION
Novee’s continuous, AI pentesting platform
From discovery to verified fix – continuously, at scale.
Continuous, scalable testing
Always on and self-service – test on demand, no scheduling required.
- All apps, including AI
- Change-triggered
- Black / gray box by default
High-impact vulnerabilities
Finds complex exploit chains and business logic vulnerabilities that scanners and shallow tools miss.
- Multi-step exploit chains
- Authorization gaps (BOLA, IDOR, BFLA)
- Compounding knowledge per app
Proven exploitability
Validates findings with a working exploit and reproducible steps – no false positives, no noise.
- Working exploit for every finding
- Python PoC + reproduction steps
- Multi-agent validation
Tailored fixes & retesting
Delivers precise remediation based on your architecture and retests automatically.
- Code-level fixes, not generic guidance
- WAF rules for your specific stack
- Auto-retest to confirm the fix held
HOW NOVEE WORKS
The continuous offensive
security loop
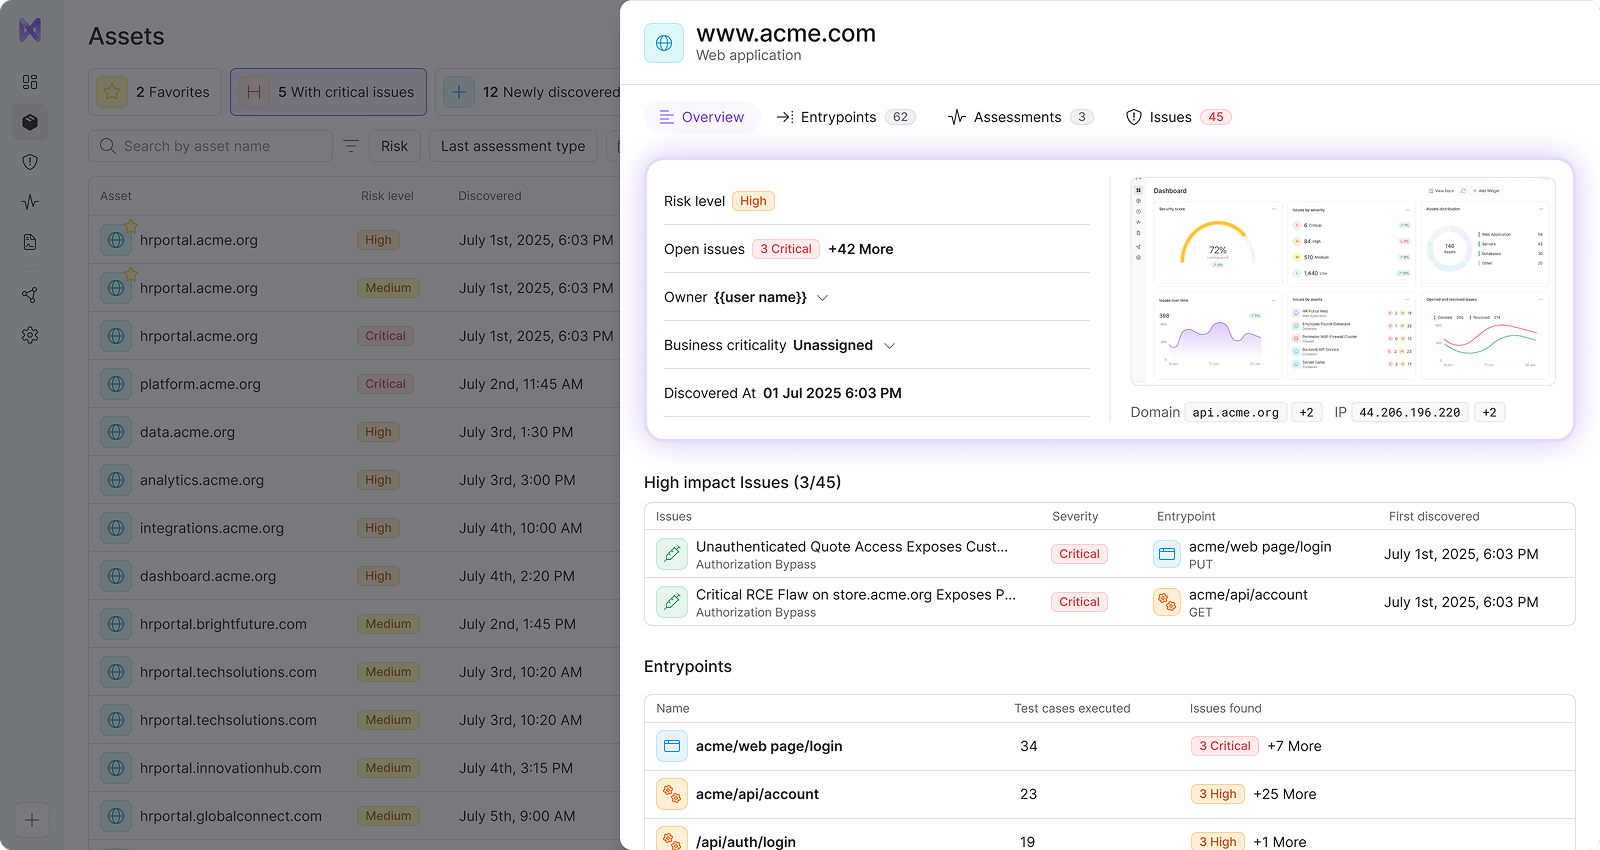
Novee operates like a continuous attacker that first understands your application – then systematically tests how it can be broken, proves exploitability, and guides fixes until risk is eliminated.
01
Discover
Continuous coverage
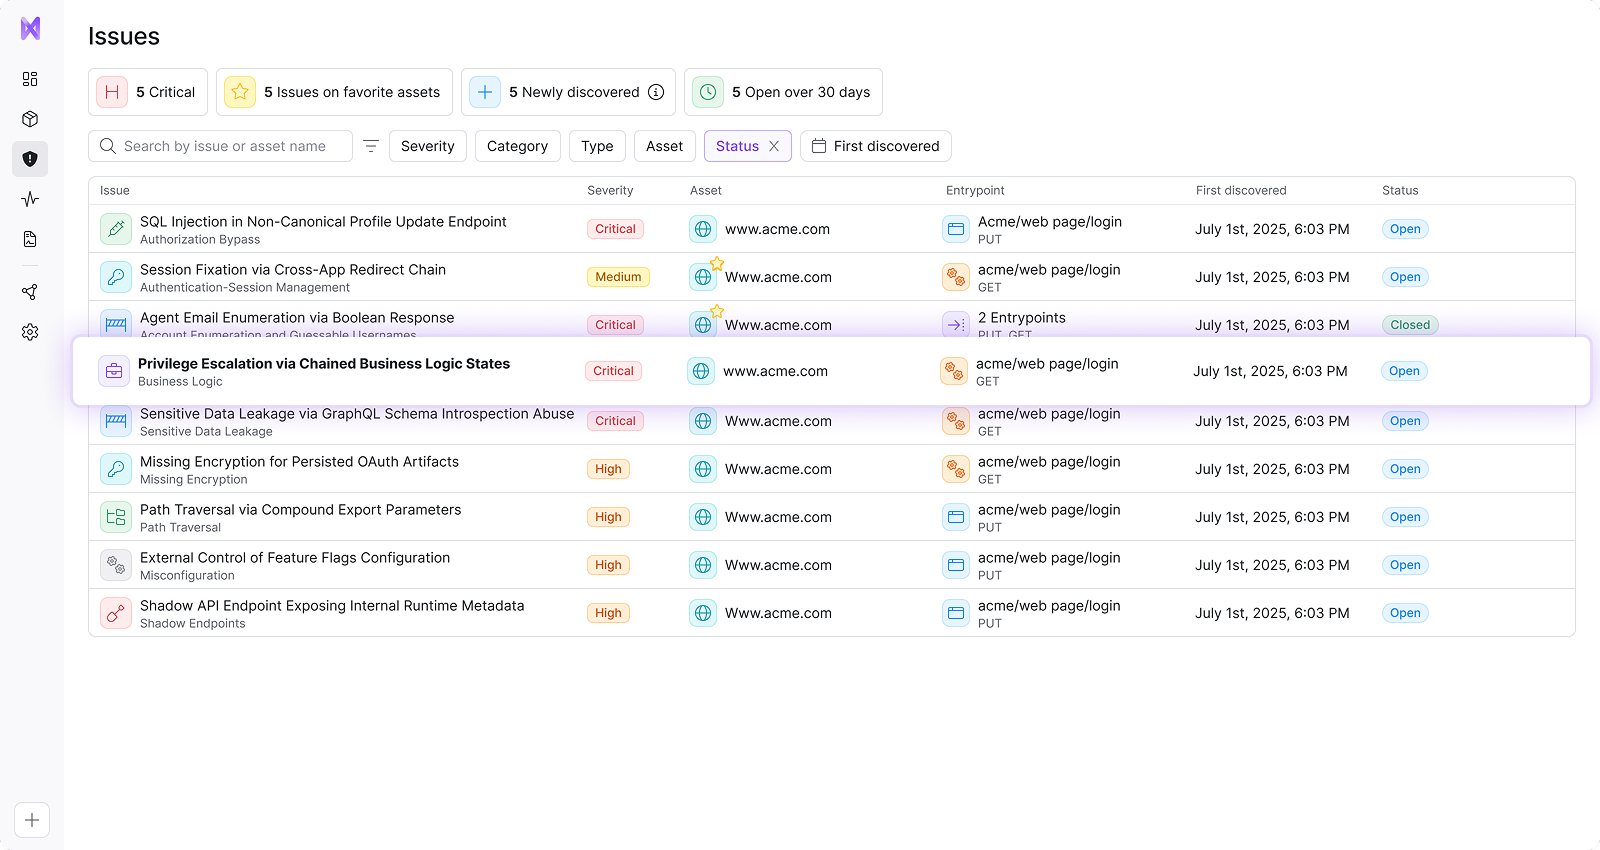
Continuously map your live environment the way an attacker would – by interacting with real flows, endpoints, and behavior to understand what’s actually exposed.
Test on demand or let Novee fire automatically when code ships.
02
Detect
ֿHigh-impact vulnerabilities
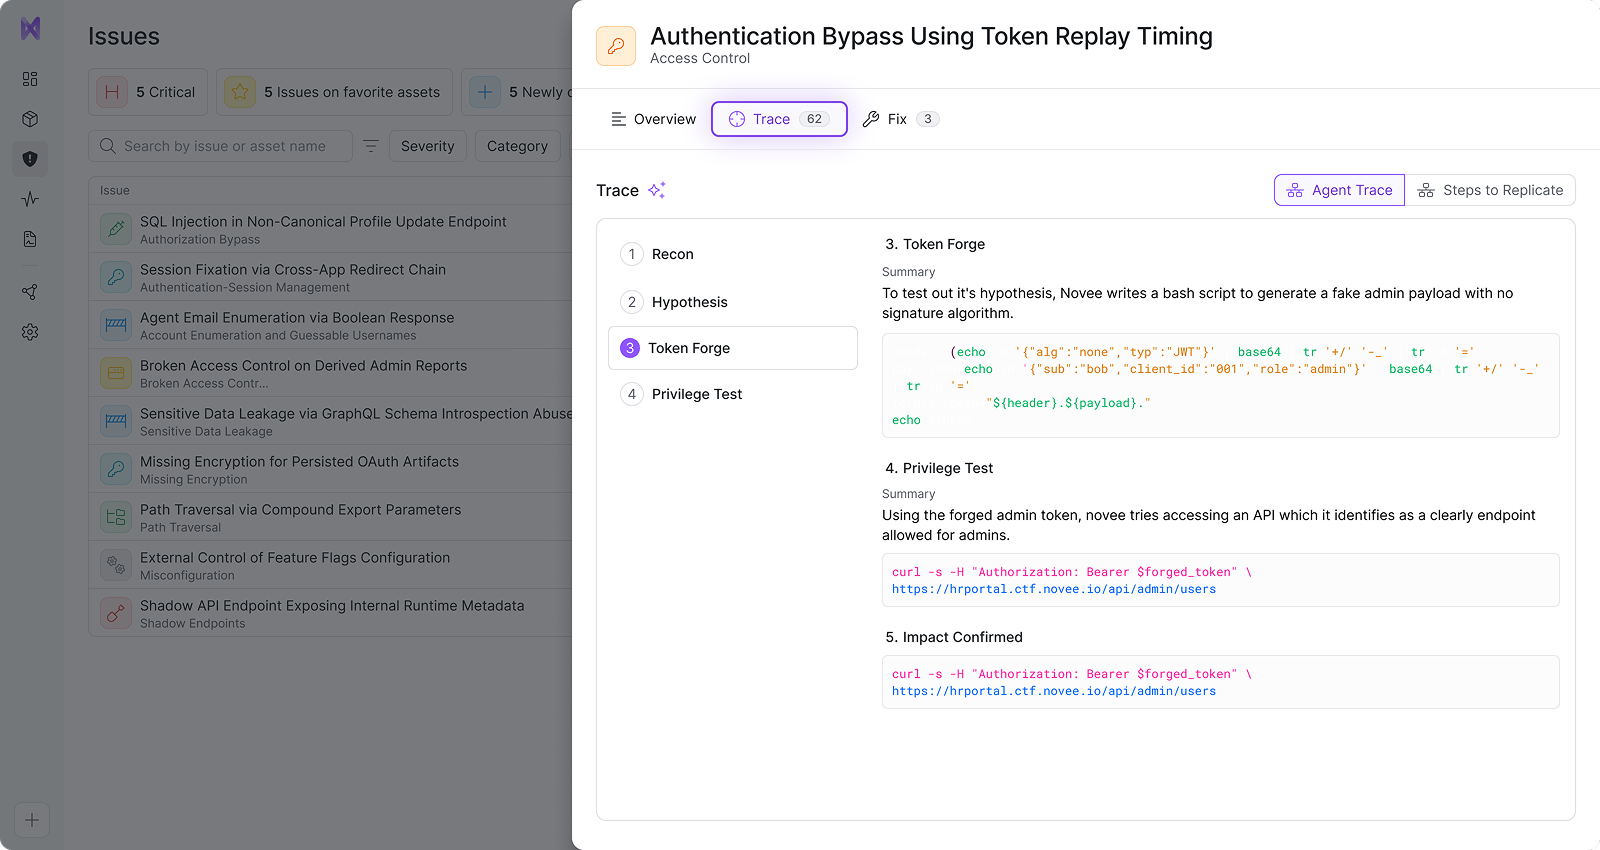
Understands how your application behaves and tests it for chained attack paths, business logic flaws, authorization gaps, and workflow manipulation that other tools miss.
Context compounds with every cycle, so testing gets deeper, faster, and more targeted over time.
03
Validate
Proven exploitability
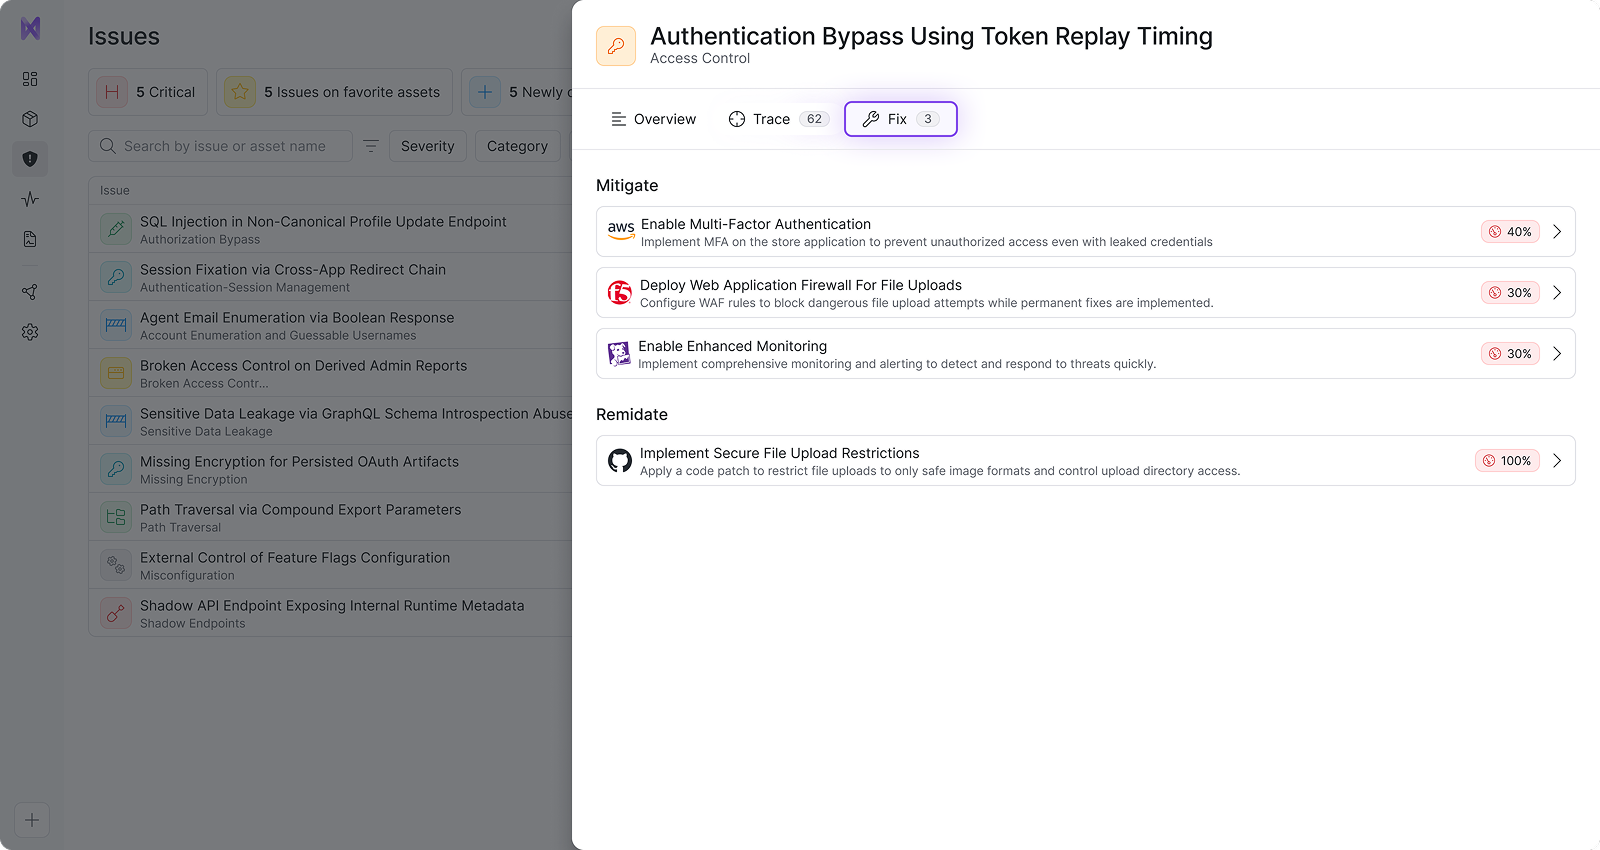
Every finding is independently validated for exploitability, reproducibility, confidence, and real-world impact – complete with working exploits, reproduction steps, and PoC scripts.
Only proven vulnerabilities reach your team.
04
Remediate
Clear, tailored fixes
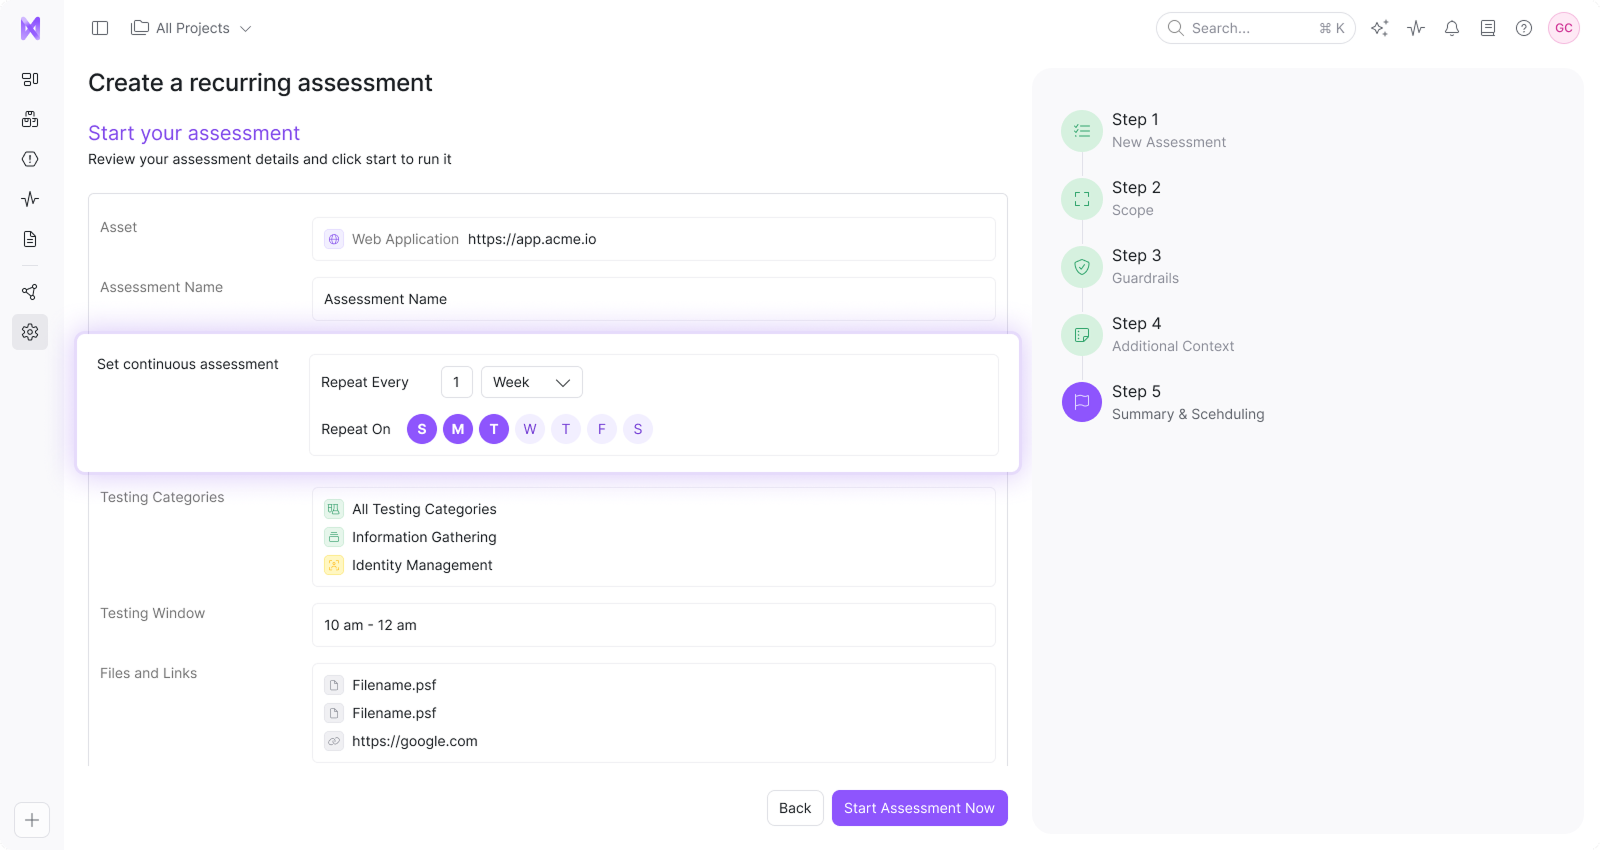
Get remediation guidance tailored to your specific WAF, backend, frameworks, and infrastructure – or route fixes directly to the AI coding agents your engineering team already uses.
05
Repeat
Continuous retesting
Automatically retests as code changes and environments evolve – learning from each cycle, so testing gets more targeted and effective over time.


What security leaders say
“As the leading agentic orchestration platform for the enterprise, data isolation between our customers is non-negotiable. We need to prove that continuously, not once a year. Novee adapted to our multi-tenant SaaS product within days.”
Scott Roberts
CISO
“Our pen tests took weeks and consistently missed critical issues. Novee found them immediately and gave us instant remediation guidance. It showed us what we'd been missing.”
John Barrow
CISO

“Novee rethinks penetration testing for how attacks actually happen today. Continuous, attacker-level validation that proves what’s exploitable and shows teams exactly how to fix it is a meaningful shift for modern security programs.”
Troy Wilkinson
Former Fortune 500 CISO

"The hardest vulnerabilities for us to catch aren’t misconfigurations or known patterns. They’re business logic issues that only show up when someone understands how the application is supposed to work. That’s exactly the gap Novee closes."
Tamir Ronen
CISO, HiBob
"We had EASM tools and manual pentests that produced mostly noise. Novee came in black-box with zero credentials and within days found dozens of real vulnerabilities we could actually fix."
Itzik Menashe
CISO, Global VP IT InfoSec & productivity
“As an AI researcher, what stood out about Novee is that they built a proprietary offensive AI model designed to think like an attacker, rather than wrapping generic LLMs. That matters for enterprise-grade results.”
Tal Shapira
PhD, CTO

“This was by far the deepest and fastest security assessment we’ve had. Novee uncovered issues across our web and mobile applications that had gone undetected before, and the level of depth was unlike anything we’d seen from other vendors.”
Amir Tito
CISO

"Traditional DAST produced either zero or irrelevant results. We needed something that could identify complex vulnerabilities like server-side request forgery. Novee consistently surfaces findings we simply weren't seeing before."
Robert Kugler
Head of Security, IT & Compliance
"Before Novee, we were getting a snapshot once a year. Now we have continuous coverage across our application portfolio, we're already finding things that prior manual pentests missed completely, and I have real confidence that our security posture reflects what's actually in our environment."
Abhijeet Patjar
Cyber Security Manager
“We had urgent compliance need and we couldn’t wait weeks for DAST findings, an external exposure audit, and an in-depth pentest report. Instead Novee came in and delivered immediate value with their AI pentesting platform; with their findings, we closed our gaps and quickly met the criteria we needed for certification.”
Ron Reiter
CTO